Understand WordPress Plugin Code Before You Trust It
WordPress plugins can legitimately access databases, write files, register REST API routes, communicate with external services, schedule background tasks, process uploads, and manage user capabilities.
The presence of these functions does not automatically mean that a plugin is vulnerable or unsafe.
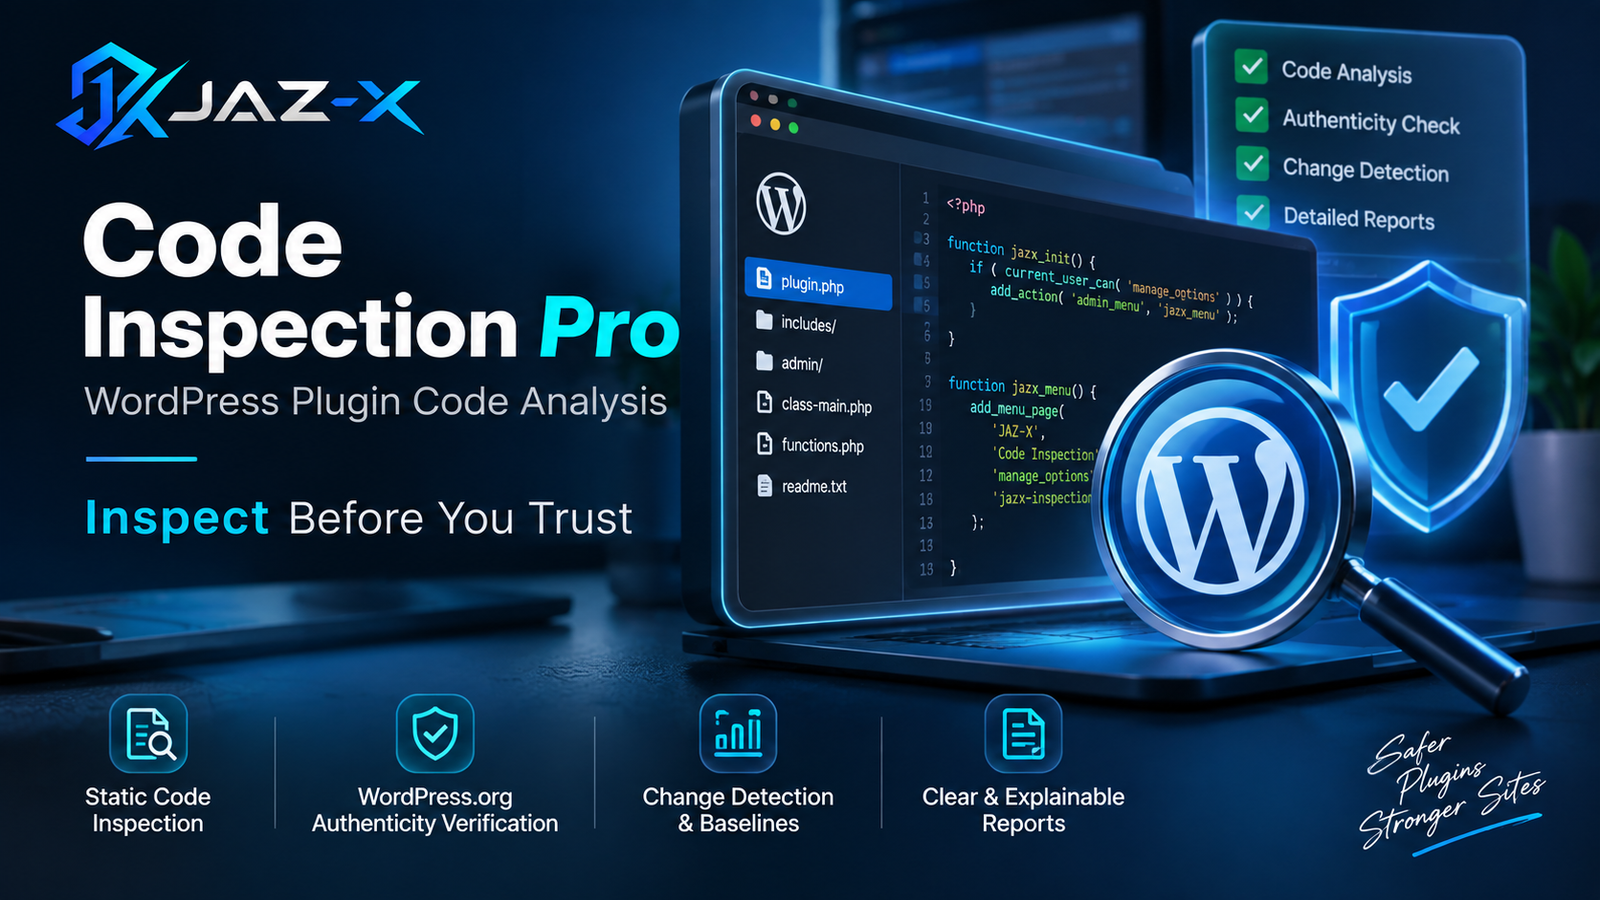
JAZ-X Code Inspection Pro is a static code inspection and analysis tool designed to help developers, website owners, agencies, maintainers, and code reviewers understand what a WordPress plugin’s source code contains and identify areas that may deserve closer review.
It analyzes plugin source files without executing the plugin code and organizes the resulting evidence into useful categories, helping you distinguish expected functionality from code patterns that warrant manual inspection.
More Than Simple Pattern Matching
JAZ-X Code Inspection Pro does not treat every powerful WordPress function or unusual code pattern as a confirmed vulnerability.
Instead, it preserves the underlying evidence while using available code context to help interpret what was found.
Reports can distinguish between:
Confirmed Vulnerabilities
Reserved for issues where sufficient static evidence is available to support the finding.
Needs Review
Code patterns or behaviors where the available evidence warrants human verification.
Expected Capabilities
Potentially powerful but legitimate WordPress functionality, including database access, REST routes, filesystem operations, scheduled jobs, outbound requests, and user or role management.
Raw Code Matches
The actual source-code locations identified during inspection. Raw matches are evidence for review and are not automatically treated as vulnerabilities.
Review Security-Relevant Code Patterns
The tool examines WordPress plugin source code for a range of security-relevant and operational patterns, including:
- REST API routes
- Unauthenticated AJAX actions
- Database operations
- Filesystem writes and deletion
- Outbound network requests
- Scheduled background tasks
- User and role changes
- Dynamic code execution
- Obfuscation patterns
- Unsafe deserialization
- Upload behavior
- Redirect behavior
- SQL-related data flows
- Output-related data flows
- Hardcoded secrets
- Weak cryptographic primitives
- Dependency-related signals
These findings provide technical evidence for inspection rather than automatically declaring a plugin malicious or compromised.
Context-Aware Code Analysis
A function name alone rarely tells the complete story.
Where applicable, JAZ-X Code Inspection Pro can consider nearby implementation details and defensive controls such as:
- Permission callbacks
- Capability checks
- Nonce protection
- Input sanitization
- Prepared SQL
- Safe redirects
- URL validation
- File validation
- Input context
- Outbound destinations
- Hash usage context
This additional context helps reviewers concentrate on findings that genuinely deserve closer inspection while preserving the underlying evidence.
Know What Changed
Reviewing a plugin once does not tell you what may change in a future version.
JAZ-X Code Inspection Pro supports trusted baselines and comparison of later scans so that meaningful changes can be identified more easily.
Comparisons can highlight:
- New findings
- Resolved findings
- Changed interpretations
- Added files
- Modified files
- Deleted files
Instead of reviewing an entire plugin from the beginning after every update, you can concentrate on what actually changed.
WordPress.org Authenticity Verification
For supported plugins distributed through WordPress.org, JAZ-X Code Inspection Pro can compare installed files with the official release information.
This helps identify whether supported plugin files correspond to the expected WordPress.org release or whether unexpected file modifications are present.
Authenticity information complements source-code inspection and baseline comparison by providing another useful piece of evidence during a code review.
Explainable Reports
JAZ-X Code Inspection Pro is designed to provide more than a simple match count.
Its reports help answer practical questions such as:
What was found?
Review the technical evidence and relevant source-code location.
Why was it identified?
Understand the capability or code behavior associated with the finding.
Are relevant controls visible?
Review nearby protections where static analysis can identify them.
Does it appear expected or require further review?
Use contextual interpretation to prioritize manual inspection.
What changed since the previous trusted scan?
Use baseline comparison to identify meaningful code and file changes.
Designed for Real-World WordPress Plugins
Large WordPress plugins can contain hundreds of powerful or security-sensitive functions as part of perfectly legitimate functionality.
Database queries, REST routes, filesystem operations, outbound requests, or cryptographic functions should not automatically be presented as vulnerabilities simply because they exist.
JAZ-X Code Inspection Pro keeps the technical evidence available while applying contextual interpretation where possible, producing reports intended to assist informed human review.
Static Inspection — No Plugin Code Execution
JAZ-X Code Inspection Pro performs static inspection of plugin source files.
The plugin being examined does not need to be executed by the inspection process for its source code to be analyzed.
This allows unfamiliar or installed plugin code to be reviewed while maintaining an important distinction:
Static-analysis findings are evidence and review signals. They are not, by themselves, proof of malware, exploitation, or compromise.
From Initial Inspection to Change Tracking
JAZ-X Code Inspection Pro combines source-code inspection with contextual interpretation, scan history, trusted baselines, file-change comparison, and supported WordPress.org authenticity verification.
This creates an ongoing code-review workflow where you can inspect what a plugin contains today and identify meaningful changes in later versions.
Inspect the code. Understand the capability. Establish a baseline. Review what changes.
Important Product Scope
JAZ-X Code Inspection Pro is a WordPress plugin source-code inspection and static analysis tool.
It is not antivirus software, a device cleaner, a computer repair utility, or a technical support service. It does not scan, clean, repair, optimize, or maintain a user’s computer or other electronic device.
Its purpose is to provide code-level evidence, contextual analysis, and change information that can assist humans when reviewing WordPress plugins.
Reviews
There are no reviews yet.